Compliance Summary
Multi-Framework Compliance Coverage Summary
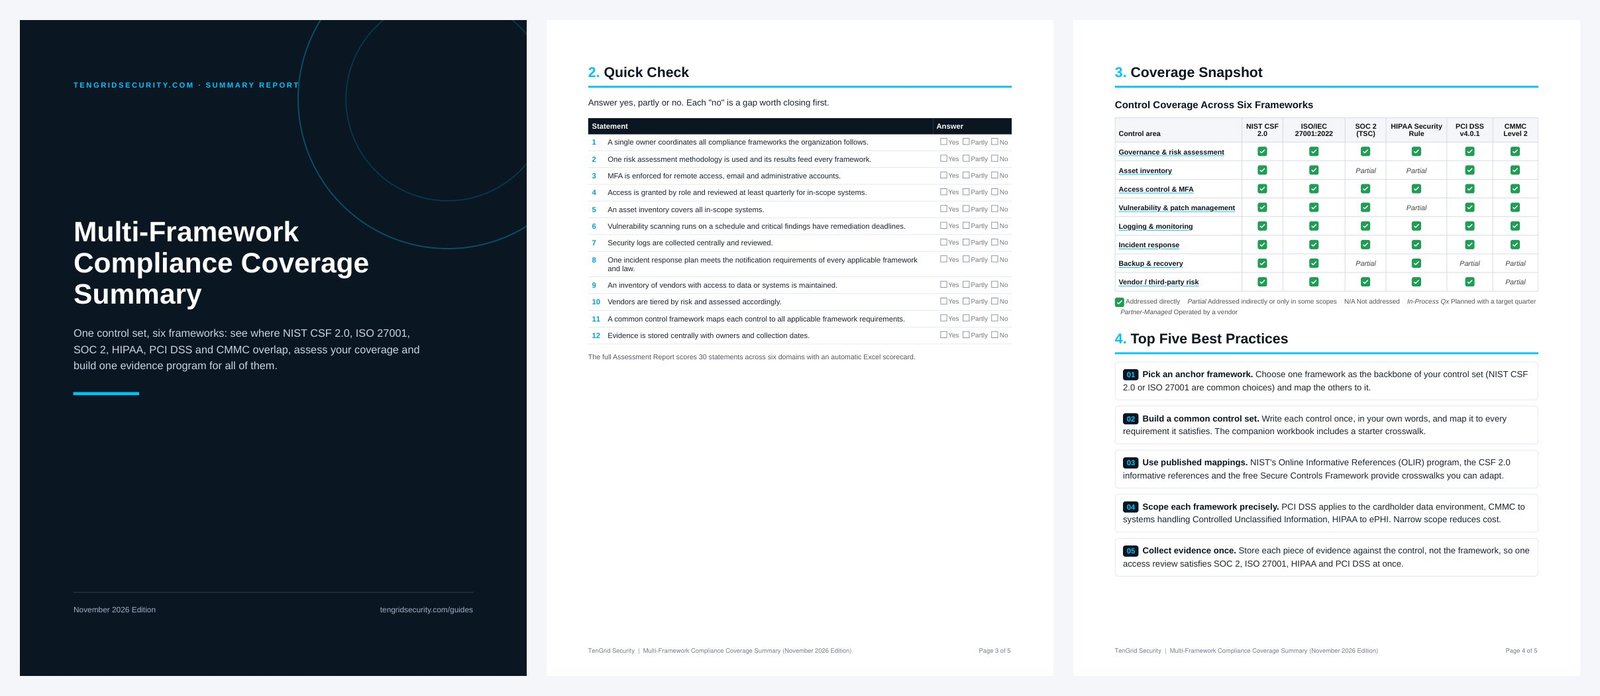
A short, 5-page overview of multi-framework compliance coverage: the key facts, a quick check, a coverage snapshot and your first 30 days.
What’s inside
- At a glance: why it matters, with three figures from published research
- A 12-question quick check (yes, partly or no)
- A coverage snapshot in a trust-center-style table
- The top five best practices
- Key lessons from public incidents
- Your first 30 days
Summary or full report?
The Summary is a fast way to brief leadership or decide where to start. The Multi-Framework Compliance Coverage Report adds a 30-question scored self-assessment, the full coverage matrix, case studies, industry analysis, review summaries, multi-source analysis, an Excel workbook, visual reports and a 30/60/90-day plan.
Who it’s for
Compliance leads, IT directors and founders who face requests for more than one framework from customers, regulators or contracts.
$50 · one-time payment · instant PDF download after purchase.
5-page PDF. Your download link appears on the order confirmation page and in your order email.
This report is an educational self-assessment guide. It is not an audit, attestation, certification, penetration test or legal advice, and completing it does not make an organization compliant with, or certified against, any framework or law. TenGrid Security is not affiliated with or endorsed by NIST, CISA, the Center for Internet Security, ISO, IEC, the AICPA, HHS, the PCI Security Standards Council, the Cloud Security Alliance or the U.S. Department of Defense. Framework and product names are used only to identify them. Coverage matrices summarize how each framework addresses a topic for planning purposes; always confirm against the official text. Case studies are drawn from public records cited in each entry. Readiness tracker tables show an example layout only and do not describe any real organization.