Compliance Assessment Report
Multi-Framework Compliance Coverage Report
One control set, six frameworks: see where NIST CSF 2.0, ISO 27001, SOC 2, HIPAA, PCI DSS and CMMC overlap, assess your coverage and build one evidence program for all of them.
What you get
- A 20-page PDF report with a 30-question scored self-assessment across six domains
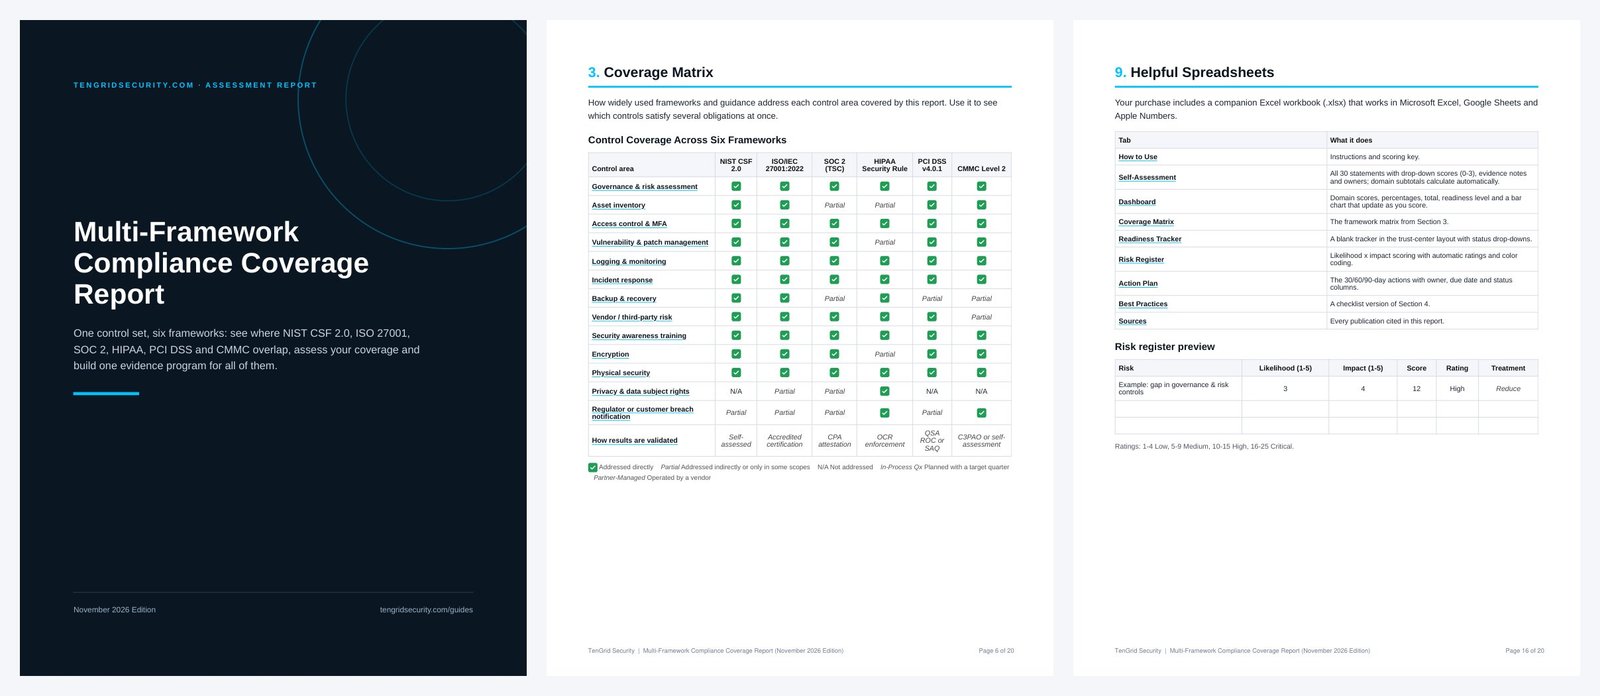
- A trust-center-style coverage matrix that shows how major frameworks address each control
- A companion Excel workbook with automatic scoring, a dashboard, a readiness tracker, a risk register and an action plan
- A 30/60/90-day action plan you can start this week
Sections in the report
- Best Practices: 10 practical steps with plain-language explanations
- Case Studies: lessons from public incidents (Equifax, Target, Anthem, Inc.), each with cited sources
- Industry Analysis: current figures and trends from published research
- Review Summaries: short summaries of the key guidance documents, with a takeaway for each
- Multi-Source Analysis: where frameworks and guidance agree, and where they differ
- Helpful Spreadsheets: the Excel workbook described above (Excel, Google Sheets or Numbers)
- Visual Reports: a domain radar, a risk heat map, a framework consensus chart and a roadmap timeline
Coverage matrix preview
Control Coverage Across Six Frameworks
| Control area | NIST CSF 2.0 | ISO/IEC 27001:2022 | SOC 2 (TSC) | HIPAA Security Rule | PCI DSS v4.0.1 | CMMC Level 2 |
|---|---|---|---|---|---|---|
| Governance & risk assessment | ||||||
| Asset inventory | Partial | Partial | ||||
| Access control & MFA | ||||||
| Vulnerability & patch management | Partial | |||||
| Logging & monitoring | ||||||
| Incident response | ||||||
| Backup & recovery | Partial | Partial | Partial | |||
| Vendor / third-party risk | Partial |
Addressed directly Partial Addressed indirectly or in some scopes N/A Not addressed. For planning only; confirm against official framework text.
Showing 8 of 14 control areas. The full matrix and a blank readiness tracker are in the report and workbook.
Who it’s for
Compliance leads, IT directors and founders who face requests for more than one framework from customers, regulators or contracts.
$150 · one-time payment · instant PDF and Excel download after purchase.
Get the Assessment Report — $150
Your download links appear on the order confirmation page and in your order email.
Want a quick overview first? Read the Multi-Framework Compliance Coverage Summary ($50) · See all guides
This report is an educational self-assessment guide. It is not an audit, attestation, certification, penetration test or legal advice, and completing it does not make an organization compliant with, or certified against, any framework or law. TenGrid Security is not affiliated with or endorsed by NIST, CISA, the Center for Internet Security, ISO, IEC, the AICPA, HHS, the PCI Security Standards Council, the Cloud Security Alliance or the U.S. Department of Defense. Framework and product names are used only to identify them. Coverage matrices summarize how each framework addresses a topic for planning purposes; always confirm against the official text. Case studies are drawn from public records cited in each entry. Readiness tracker tables show an example layout only and do not describe any real organization.